OpenVAS, a half of Greenbone Networks, is an open-source vulnerability scanner that provides a full-featured answer for organizations of all sizes. It frequently updates its detection capabilities to keep pace with new threats. It can also be used for intrusion detection, making it a versatile tool for cybersecurity professionals on a budget.
You get zero false positives as a outcome of RidgeBot® validates vulnerabilities by actually exploiting them rather than just scanning for them. Mature steady safety validation applications mix a quantity of complementary testing methods quite than counting on a single software. Every method covers gaps left by the others, so the combination matters greater than any individual functionality.
- Here’s a breakdown of the key AST types used in manufacturing workflows, along with software examples (you’ll find detailed device evaluations within the sections below via bookmarks).
- Traditional security testing produces a snapshot; continuous safety validation produces a pattern line.
- The tool grouped related points like lacking CSP headers, relaxed CORS insurance policies, and DOM-based vectors, which helped in trace systemic gaps in frontend sanitization logic.
- The tougher problem is deciding which exposures can be utilized by an attacker, which controls would interrupt the attack and which fixes should be prioritized first.
- As attacks grow more refined, regularly scanning your setting is crucial for shielding delicate data, avoiding breaches, and meeting regulatory necessities.
View A Pattern Ridgebot Business Risk-based Safety Report
The application provides us with great convenience and confidence in our work. A very successful platform where http://i-docs.org/bibliography/gaining-control-over-the-loss-of-it-software-as-focusing-media-in-digital-visual-ethnography/ we are ready to take a look at the accuracy of our security investments and see their scores. Re-test to substantiate the risk is gone and prove your risk has actually been decreased. In an ocean of vulnerabilities, prioritize those that are proven to endanger your corporation.

Attackiq Enterprise
By deploying automation platforms, organizations can conduct validation at frequent intervals with minimal useful resource overhead. Steady checks also mean that any modifications within the environment—such as new deployments, patches, or configuration changes—are quickly included into validation processes, preventing new exposures from lingering unnoticed. While using multiple vulnerability scanners is important in securing your techniques, relying on periodic scans leaves gaps. Steady, real-time monitoring of vulnerabilities is critical to stay forward of threats. Acunetix focuses on web utility vulnerability scanning, making it best for organizations centered on net security.
How Does Automated Security Validation Work Together With An Current Vulnerability Management Program?+
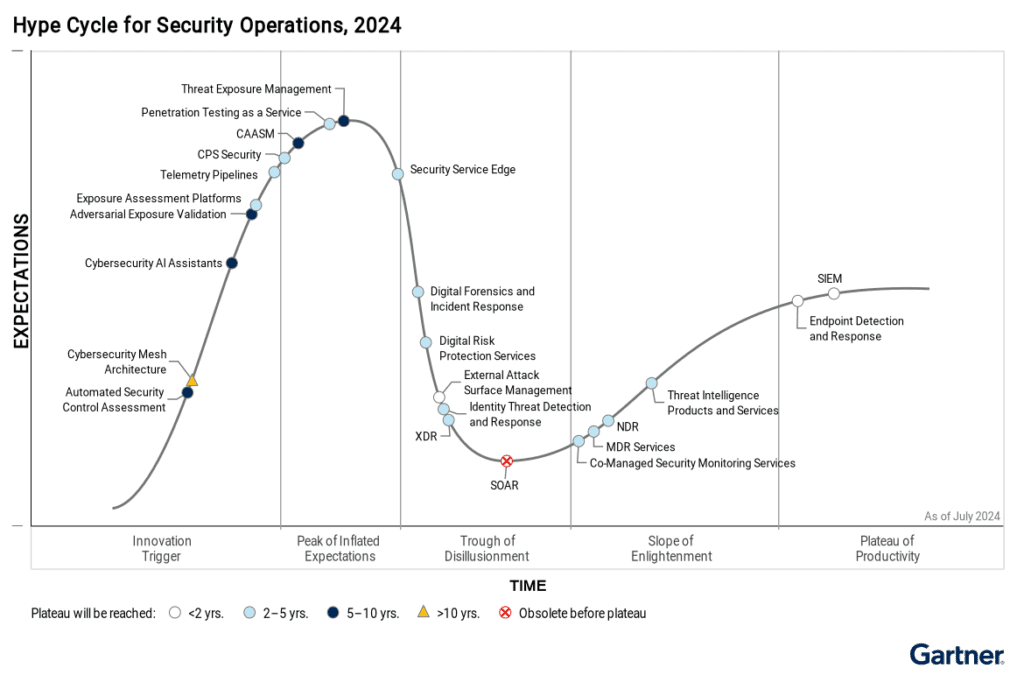
Automated safety validation is a continuous, automated process that exams your security controls and exposures by safely emulating how an actual attacker behaves inside your environment. Somewhat than cataloguing weaknesses, it tries to take advantage of them, then reviews what actually labored. Because the attack floor adjustments continuously, CyCognito monitors for brand spanking new assets, configuration drift and rising exposure, then routinely re applies relevant tests. As groups update WAF rules or modify CNAPP and CAASM insurance policies, the platform retests affected assets and reveals which gaps have closed and which controls proceed to underperform.
What Measurement Organization Benefits Most From Automated Safety Validation?+
Invicti also supports multi-tenant environments, centralized policy administration, and SLA-based reporting, which makes it significantly efficient for organizations with distributed utility safety possession. Burp Suite is a DAST tool extensively used by penetration testers, pink groups, and AppSec engineers to find vulnerabilities in live internet purposes. Developed by PortSwigger, it provides a mixture of handbook control and automated scanning, giving groups full flexibility to simulate advanced attack flows in real-world circumstances. Security validation is designed to test the tools and controls an organization already has in place. It identifies the place current firewalls, endpoint protection, identification controls or cloud security tools are underperforming, quite than requiring a wholesale substitute.
James Walker is a content writer and language researcher with over 5 years of experience in meanings, definitions, and language-related topics. He enjoys simplifying complex terms into clear, easy-to-understand explanations. Through ZoopNestly.com, he helps readers find accurate and reliable information.
Leave a Reply